Journals and Books

Building Adaptative and Transparent Cyber Agents with Local Language Models

Building Adaptative and Transparent Cyber Agents with Local Language Models

Autonomous intelligent agents offer a transformative approach to cyber defense by operating independently in complex and dynamic environments. While much research has focused on defensive systems, offensive agents are equally important for testing system resilience and improving defenses through realistic adversarial interaction. Recent advances demonstrate that large language models can automate penetration testing effectively, rivaling traditional reinforcement learning methods, but their reliance on cloud-based services introduces significant concerns around privacy and reproducibility.
AlquistCoder: A Synthetic Data Approach to Training Compact Secure Coding Assistants and Building Security Benchmarks

AlquistCoder: A Synthetic Data Approach to Training Compact Secure Coding Assistants and Building Security Benchmarks

Large language models are increasingly used as programming assistants, but their security behavior remains uneven: they may generate code with vulnerable patterns, and they may provide actionable help for malicious requests. This paper introduces AlquistCoder, a compact 3.8B‐parameter coding assistant designed to address both risks through targeted synthetic‐data alignment.

Building Adaptative and Transparent Cyber Agents with Local Language Models

Building Adaptative and Transparent Cyber Agents with Local Language Models

Autonomous intelligent agents offer a transformative approach to cyber defense by operating independently in complex and dynamic environments. While much research has focused on defensive systems, offensive agents are equally important for testing system resilience and improving defenses through realistic adversarial interaction. Recent advances demonstrate that large language models can automate penetration testing effectively, rivaling traditional reinforcement learning methods, but their reliance on cloud-based services introduces significant concerns around privacy and reproducibility.
CTU Hornet 65 Niner: A Network Dataset of Geographically Distributed Low-Interaction Honeypots

CTU Hornet 65 Niner: A Network Dataset of Geographically Distributed Low-Interaction Honeypots

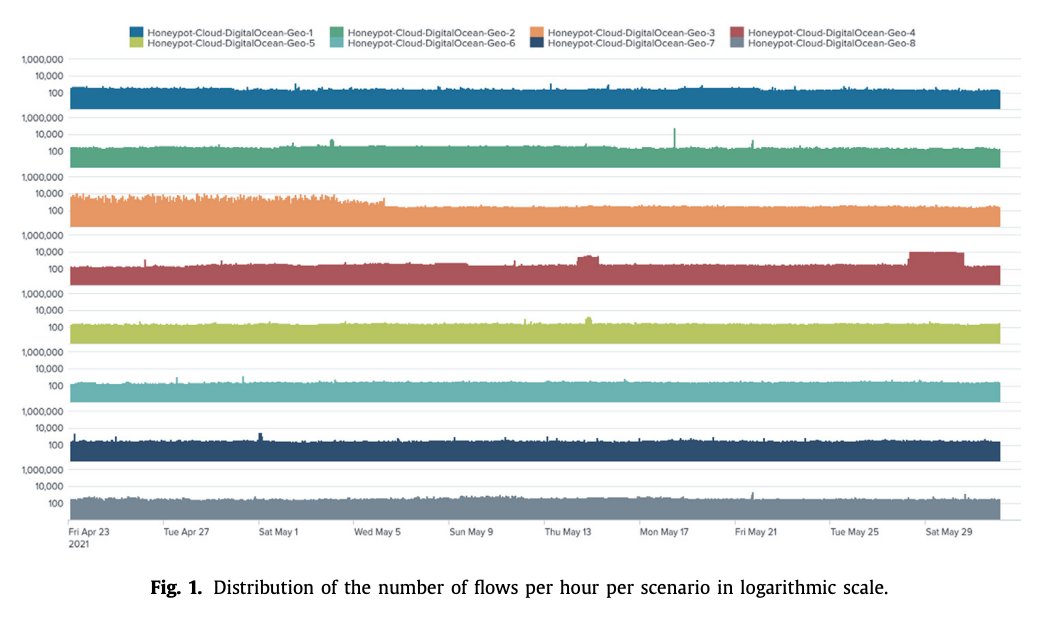
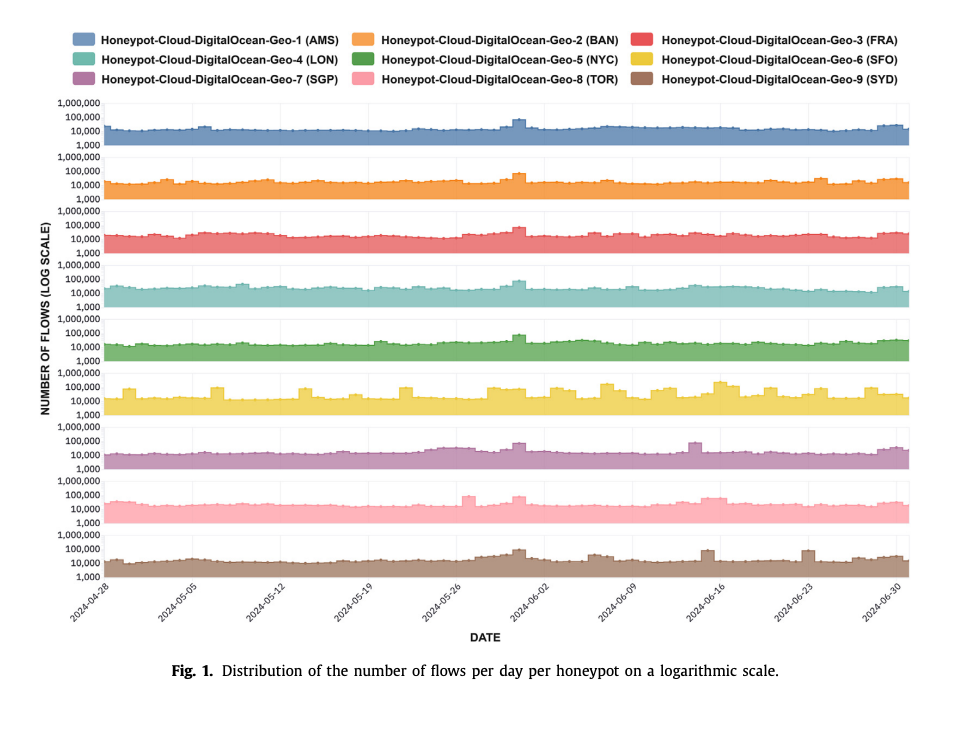
This data article introduces a new network dataset created to help understand how geographical location impacts the quality, type, and amount of incoming network attacks received by honeypots. The dataset consists of 12.4 million network flows collected from nine low-interaction honeypots in nine cities across the world for 65 days, from April 29th to July 1st, 2024. Each low-interaction honeypot was identically configured to capture incoming attacks using a state-of-the-art network flow collector, Zeek. Honeypots were distributed in nine cities: Amsterdam, Bangalore, Frankfurt, London, New York, San Francisco, Singapore, Toronto, and Sydney. The dataset is in JSON format and contains all types of Zeek network flow files, including protocol-specific logs.

Conti Inc.: Understanding the Internal Discussions of a Large Ransomware-as-a-Service Operator with Machine Learning

Conti Inc.: Understanding the Internal Discussions of a Large Ransomware-as-a-Service Operator with Machine Learning

This paper analyzes the main discussion topics in the Conti chat leak using machine learning techniques such as Natural Language Processing (NLP) and Latent Dirichlet Allocation (LDA), as well as visualization strategies. Five discussion topics are found: (1) Business, (2) Technical, (3) Internal tasking/Management, (4) Malware, and (5) Customer Service/Problem Solving. Moreover, the distribution of topics among Conti members shows that only 4% of individuals have specialized discussions while almost all individuals (96%) are all-rounders, meaning that their discussions revolve around the five topics.

A Survey of Privacy Attacks in Machine Learning

A Survey of Privacy Attacks in Machine Learning

As machine learning becomes more widely used, the need to study its implications in security and privacy becomes more urgent. Although the body of work in privacy has been steadily growing over the past few years, research on the privacy aspects of machine learning has received less focus than the security aspects. Our contribution in this research is an analysis of more than 45 papers related to privacy attacks against machine learning that have been published during the past seven years. We propose an attack taxonomy, together with a threat model that allows the categorization of different attacks based on the adversarial knowledge, and the assets under attack. An initial exploration of the causes of privacy leaks is presented, as well as a detailed analysis of the different attacks. Finally, we present an overview of the most commonly proposed defenses and a discussion of the open problems and future directions identified during our analysis.

Stealing and Evading Malware Classifiers and Antivirus at Low False Positive Conditions

Stealing and Evading Malware Classifiers and Antivirus at Low False Positive Conditions

Model stealing attacks have been successfully used in many machine learning domains, but there is little understanding of how these attacks work against models that perform malware detection. Malware detection and, in general, security domains have unique conditions. In particular, there are very strong requirements for low false positive rates (FPR). Antivirus products (AVs) that use machine learning are very complex systems to steal, malware binaries continually change, and the whole environment is adversarial by nature. This study evaluates active learning model stealing attacks against publicly available stand-alone machine learning malware classifiers and also against antivirus products.

On the Dynamics Behind Profit-Driven Cybercrime: From Contextual Factors to Perceived Group Structures, and the Workforce at the Periphery

On the Dynamics Behind Profit-Driven Cybercrime: From Contextual Factors to Perceived Group Structures, and the Workforce at the Periphery

Through an inductive thematic analysis of semi-structured interviews with experts, this study corroborates key findings on contextual and organisational dynamics behind profit-driven cybercrime. The findings pinpoint three contextual factors influencing individuals to participate in profit-driven cybercrime: lack of legal economic opportunities, lack of deterrents, and drifting means. The findings also highlight how experts perceive group structures of those behind profit-driven cybercrime: as organised, enterprise-like, loose networks, or communities. Experts’ narratives, moreover, emphasise the presence of a workforce at the periphery of cybercrime groups. Such a workforce is not actively involved in developing criminal schemes, yet it helps their orchestration by achieving necessary tasks such as writing texts or developing software. The study results confirm key insights on crime participation related to both cyber and non-cybercrime literature while also raising new research avenues, including questions concerning to what extent those forming the peripheral workforce are willing to participate in cybercrime.

On the Motivations and Challenges of Affiliates Involved in Cybercrime

On the Motivations and Challenges of Affiliates Involved in Cybercrime

The cybercrime industry is characterised by work specialisation to the point that it has become a volume industry with various “as-a-service” offerings. One well-established “as-a-service” business model is blackmarket pay-per-install (PPI) services, which outsource the spread of malicious programmes to affiliates. Such a business model represents the archetype of specialisation in the cybercrime industry: a mass of individuals, known as affiliates, specialise in spreading malware on behalf of a service. Extant literature has focused on understanding the scope of such a service and its functioning. However, despite the large number and aggregate effect of affiliates on cybercrime, little research has been done on understanding why and how affiliates participate in such models. This study depicts the motivations and challenges of affiliates spreading Android banking Trojan applications through a blackmarket PPI service. We conducted a thematic analysis of over 6,000 of their private chat messages. The findings highlight affiliates’ labour-intensive work and precarious working conditions along with their limited income, especially compared to their expectations. Affiliates’ participation in cybercrime was found to be entangled between legal and blackmarket programmes, as affiliates did not care about programmes’ legal status as long as they yielded money. This study contributes to the literature by providing additional evidence on the downsides of work specialisation emerging from the cybercrime industry.

Hornet 40: Network Dataset of Geographically Placed Honeypots

Hornet 40: Network Dataset of Geographically Placed Honeypots

Deception technologies, and honeypots in particular, have been used for decades to understand how cyber attacks and attackers work. A myriad of factors impact the effectiveness of a honeypot. However, very few is known about the impact of the geographical location of honeypots on the amount and type of attacks. Hornet 40 is the first dataset designed to help understand how the geolocation of honeypots may impact the inflow of network attacks. The data consists of network flows in binary and text format, with up to 118 features, including 480 bytes of the content of each flow. They were created using the Argus flow collector. The passive honeypots are IP addresses connected to the Internet and do not have any honeypot software running, so attacks are not interactive. The data was collected from identically configured honeypot servers in eight locations: Amsterdam, Bangalore, Frankfurt, London, New York, San Francisco, Singapore, and Toronto. The dataset contains over 4.7 million network flows collected during forty days throughout April, May, and June 2021.

Entanglement: Cybercrime Connections of a Public Forum Population

Entanglement: Cybercrime Connections of a Public Forum Population

Many activities related to cybercrime operations do not require much secrecy, such as developing websites or translating texts. This research provides indications that many users of a popular public internet marketing forum have connections to cybercrime. It does so by investigating the involvement in cybercrime of a population of users interested in internet marketing, both at a micro and macro scale. The research starts with a case study of three users confirmed to be involved in cybercrime and their use of the public forum. It provides a first glimpse that some business with cybercrime connections is being conducted in the clear.

Detecting Botnet Traffic from a Single Host

Detecting Botnet Traffic from a Single Host

The detection of bots and botnets in the network may be improved if the analysis is done on the traffic of one bot alone. While a botnet may be detected by correlating the behavior of several bots in a large amount of traffic, one bot alone can be detected by analyzing its unique trends in less traffic. The algorithms to differentiate the traffic of one bot from the normal traffic of one computer may take advantage of these differences. The authors propose to detect bots in the network by analyzing the relationships between flow features in a time window. The technique is based on the Expectation-Maximization clustering algorithm. To verify the method they designed test-beds and obtained a dataset of six different captures. The results are encouraging, showing a true positive error rate of 99.08% with a false positive error rate of 0.7%.

Observer effect: How Intercepting HTTPS traffic forces malware to change their behavior

During the last couple of years there has been an important surge on the use of HTTPs by malware. The reason for this increase is not completely understood yet, but it is hypothesized that it was forced by organizations only allowing web traffic to the Internet. Using HTTPs makes malware behavior similar to normal connections. Therefore, there has been a growing interest in understanding the usage of HTTPs by malware. This paper describes our research to obtain large quantities of real malware traffic using HTTPs, our use of man-in-the-middle HTTPs interceptor proxies to open and study the content, and our analysis of how the behavior of the malware changes after being intercepted. The research goal is to understand how malware uses HTTPs and the impact of intercepting its traffic. We conclude that the use of an interceptor proxy forces the malware to change its behavior and therefore should be carefully considered before being implemented.

An Empirical Comparison of Botnet Detection Methods

The results of botnet detection methods are usually presented without any comparison. Although it is generally accepted that more comparisons with third-party methods may help to improve the area, few papers could do it. Among the factors that prevent a comparison are the difficulties to share a dataset, the lack of a good dataset, the absence of a proper description of the methods and the lack of a comparison methodology. This paper compares the output of three different botnet detection methods by executing them over a new, real, labeled and large botnet dataset.

Survey on Network-based Botnet Detection Methods.

Botnets are an important security problem on the Internet. They continuously evolve their structure, protocols and attacks. This survey analyzes and compares the most important efforts done in the network-based detection area. It accomplishes four tasks: first, the comparison of previous surveys and the proposal of four new dimensions to analyze their classification schemes. Second, a new classification and comparison of network-based botnet detection proposals, that includes the definition of twenty desired properties of every botnet detection paper. Third, an extensive comparison between the most representative detection proposals. Fourth, the description of the most important problems and highlights in the area. We conclude that the area has achieved great advances so far, but there are still many open problems.