This research provides the first overview of such automatic service, which takes advantage of the whole malware-as-aservice industry, providing medium quality obfuscation for the Android malware market. Although the technical obfuscations are not state-of-the-art, the service succeeds in reducing detection for malicious Android applications. We conclude that the active use of the service highlights the need for the malware market to develop better obfuscation techniques, hence the good job that the security community is doing at quickly detecting changing malware. We also conclude that this service seemed to generate enough revenue for the group, given its automatic nature and purpose. Given that automatic services like this may be a greater problem in the future of malware obfuscation, this research provides a first technical analysis of the details of such obfuscation service and the possible impact in detection results.
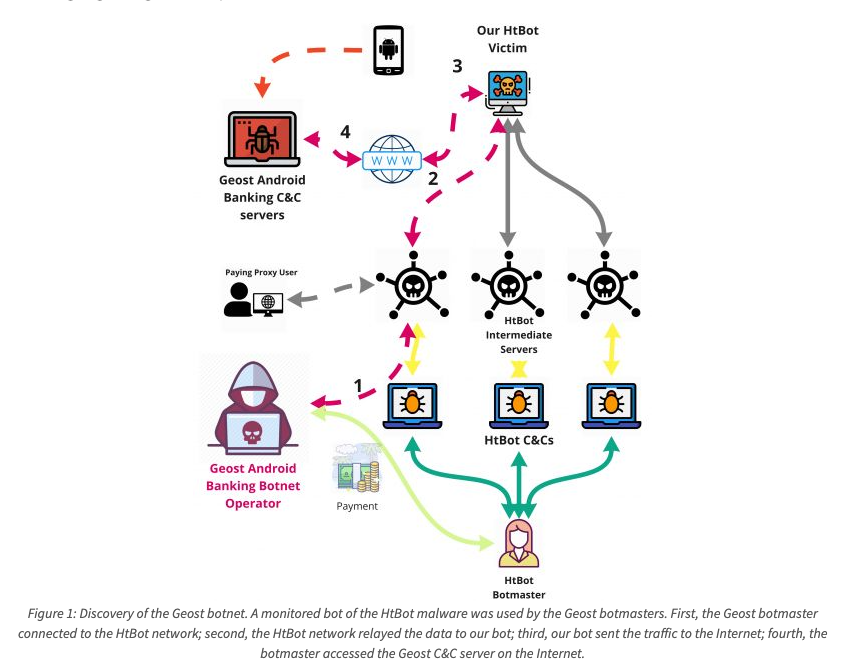
Geost botnet. The story of the discovery of a new Android banking trojan from an OpSec error
This paper describes an ew botnet, which we called Geost, discovered thanks to multiple OpSec mistakes made by the attackers. The mistakes included: the use of the HtBot malware’s illegal proxy network; failing to encrypt the command-and-control servers; re-using security services; trusting other attackers that practise even less operational security; and failing to encrypt chat sessions. As far as we know, the Geost botnet has hundreds of malicious domains, 13 C&C servers, approximately 800,000 victims in Russia, and potential access to several million Euros in bank accounts.
A Study of Machete Cyber Espionage Operations in Latin America
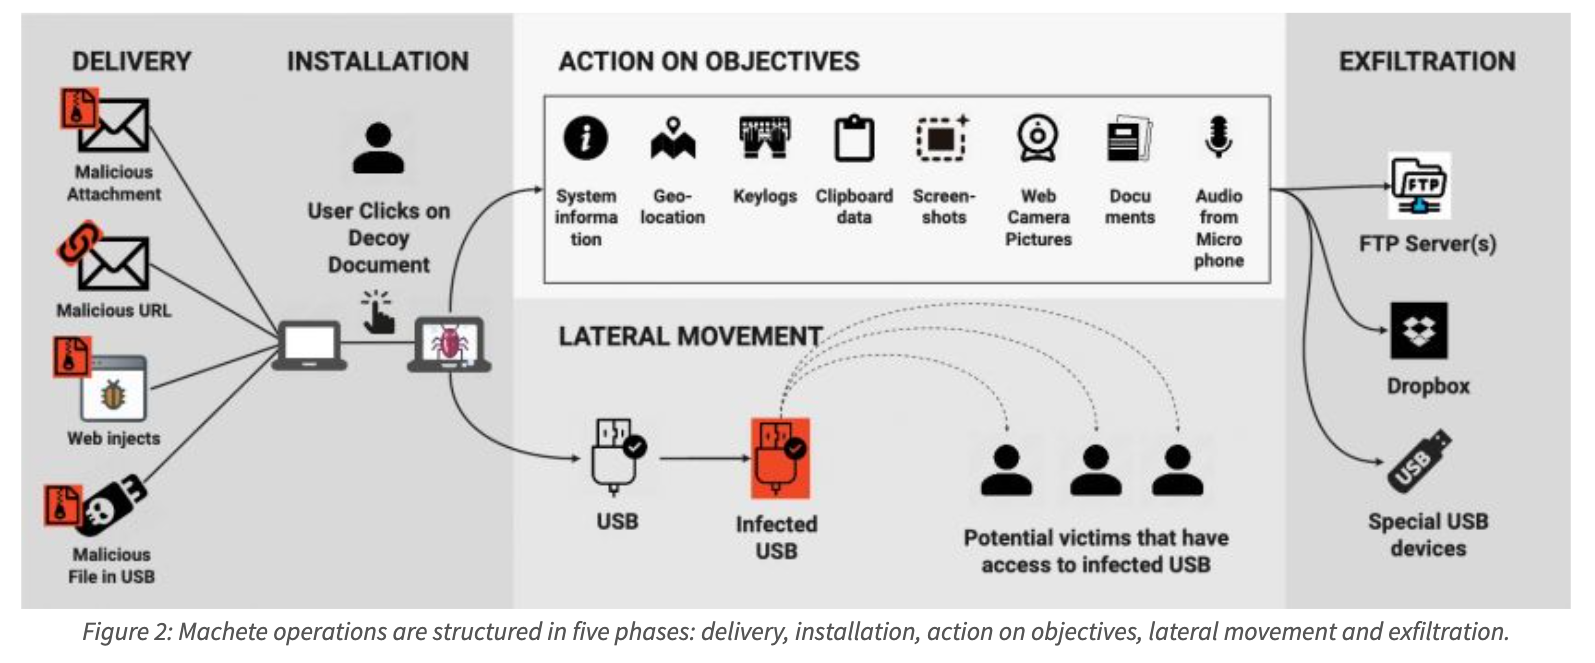
Our research shows that Machete is operated by a highly coordinated and organized group that focuses on Latin American targets. We describe the five phases of the APT operations from delivery to exfiltration of information and we show why Machete is considered a cyber espionage tool. Furthermore, our analysis indicates that the targeted victims belong to military, political or diplomatic sectors. The review of the almost eight years of Machete operations shows that it is probably operated by a single group whose activities may be state-sponsored. Machete is still active and operational to this day.
Modelling the Network Behaviour of Malware to Block Malicious Patterns. The Stratosphere Project: A Behavioural IPS
Current malware traffic detection solutions work mostly by using static fingerprints, white and black lists and crowd-sourced threat intelligence analytics. These methods are useful for detecting known malware in real time, but are insufficient for detecting unknown malicious trends and attacks. Our proposed complementary solution is to analyse the inherent patterns of malware actions in the network by means of machine learning algorithms. In particular, we use Markov chains-based algorithms to find network patterns that are independent of static features, such as IP addresses or payloads.
Arming Malware with GANs
Generative Adversarial Networks (GANs) are a recent invention that shows impressive results in generating completely new images of faces, building interiors and much more. In this talk we present how we can use GANs to modify network traffic parameters in order to mimic other types of traffic. More specifically, we modify an open source malware to use a GAN to dynamically adapt its Command and Control network behavior and mimic the traffic characteristics of Facebook chat. In this way it is able to avoid the detection from new-generation Intrusion Prevention Systems that use behavioral characteristics. We will present our experiments from a real-life scenario that used the Stratosphere behavioral IPS deployed in a router between the malware which was deployed in our lab and the C&C server deployed in AWS. Results show that it is possible for the malware to become undetected when given the input parameters from a GAN. The malware is also aware of whether or not it is being blocked and uses this as a feedback signal in order to improve the GAN model. Finally, we discuss the implications of this work in malware detection as well as other areas such as censorship circumvention.
The Network Behavior of Targeted Attacks. Models for Malware Identification and Detection.
The network patterns of Targeted Attacks is very different from the usual malware because of the different attacker’s goals. Therefore, it is difficult to detect targeted attacks looking for DNS anomalies, DGA traffic or HTTP patterns. However, our analysis of targeted attacks reveals novel patterns in their network communication. These patterns were incorporated into our Stratosphere IPS in order to model, identify and detect the traffic of targeted attacks. With this knowledge it is possible to alert attacks in the network within a short time, independently of the malware used. The Stratosphere project analyzes the inherent patterns of malware actions in the network using Machine Learning. It uses Markov Chains algorithms to find patterns that are independent of static features. These patterns are used to build behavioral models of malware actions that are later used to detect similar traffic in the network. The tool and datasets are freely published.
Modelling the Network Behaviour of Malware To Block Malicious Patterns
Current malware traffic detection solutions work mostly by using static fingerprints, white and black lists and crowd-sourced threat intelligence analytics. These methods are useful for detecting known malware in real time, but are insufficient for detecting unknown malicious trends and attacks. Our proposed complementary solution is to analyse the inherent patterns of malware actions in the network by means of machine learning algorithms. In particular, we use Markov chains-based algorithms to find network patterns that are independent of static features, such as IP addresses or payloads. These patterns are used to build behavioural models of malware actions that are later used to detect similar traffic in the network. All these models and detection algorithms have been used to create a free software intrusion prevention system called Stratosphere IPS, which has been thoroughly tested with normal and malware traffic. The IPS is able to detect new network patterns that are similar to known malicious behaviours. The Stratosphere IPS tool will be used to show how behavioural models can detect real malware traffic.