Autonomous intelligent agents offer a transformative approach to cyber defense by operating independently in complex and dynamic environments. While much research has focused on defensive systems, offensive agents are equally important for testing system resilience and improving defenses through realistic adversarial interaction. Recent advances demonstrate that large language models can automate penetration testing effectively, rivaling traditional reinforcement learning methods, but their reliance on cloud-based services introduces significant concerns around privacy and reproducibility.
Out of the Cage: How Stochastic Parrots Win in Cyber Security Environments
Large Language Models (LLMs) have gained widespread popularity across diverse domains involving text generation, summarization, and various natural language processing tasks. Despite their inherent limitations, LLM-based designs have shown promising capabilities in planning and navigating open-world scenarios. This paper introduces a novel application of pre-trained LLMs as agents within cybersecurity network environments, focusing on their utility for sequential decision-making processes.
AlquistCoder: A Synthetic Data Approach to Training Compact Secure Coding Assistants and Building Security Benchmarks
Large language models are increasingly used as programming assistants, but their security behavior remains uneven: they may generate code with vulnerable patterns, and they may provide actionable help for malicious requests. This paper introduces AlquistCoder, a compact 3.8B‐parameter coding assistant designed to address both risks through targeted synthetic‐data alignment.
Building Adaptative and Transparent Cyber Agents with Local Language Models
Autonomous intelligent agents offer a transformative approach to cyber defense by operating independently in complex and dynamic environments. While much research has focused on defensive systems, offensive agents are equally important for testing system resilience and improving defenses through realistic adversarial interaction. Recent advances demonstrate that large language models can automate penetration testing effectively, rivaling traditional reinforcement learning methods, but their reliance on cloud-based services introduces significant concerns around privacy and reproducibility.
DeepRed: A Deep Learning–Powered Command and Control Framework for Multi-Stage Red Teaming Against ML-based Network Intrusion Detection Systems
Emerging studies demonstrate that machine learning (ML) has the potential to improve the detection capabilities of network intrusion detection systems (NIDS) against evolving cyber threats. However, recent adversarial ML (AML) studies have revealed critical ML vulnerabilities. This paper presents innovative multistage red-teaming techniques to evaluate the robustness of ML-NIDS in real-world adversarial settings.
Prompt. Exploit. Repeat: Automating Network Security Testing with LLMs
Large Language Models (LLMs) have demonstrated remarkable capabilities in various tasks, but their potential in cybersecurity remains largely unexplored. Despite their inherent limitations, LLM-based designs have shown promising ability in planning and navigating open-world scenarios. This paper investigates the application of pre-trained LLMs as agents in network security environments, a domain traditionally dominated by reinforcement learning (RL) approaches. We introduce a novel method that leverages LLMs for sequential decision-making in cybersecurity scenarios, that is flexible and does not need re-training to adapt to new scenarios.
A Survey of Privacy Attacks in Machine Learning
As machine learning becomes more widely used, the need to study its implications in security and privacy becomes more urgent. Although the body of work in privacy has been steadily growing over the past few years, research on the privacy aspects of machine learning has received less focus than the security aspects. Our contribution in this research is an analysis of more than 45 papers related to privacy attacks against machine learning that have been published during the past seven years. We propose an attack taxonomy, together with a threat model that allows the categorization of different attacks based on the adversarial knowledge, and the assets under attack. An initial exploration of the causes of privacy leaks is presented, as well as a detailed analysis of the different attacks. Finally, we present an overview of the most commonly proposed defenses and a discussion of the open problems and future directions identified during our analysis.
The Power of MEME: Adversarial Malware Creation with Model-Based Reinforcement Learning
Due to the proliferation of malware, defenders are increasingly turning to automation and machine learning as part of the malware detection toolchain. However, machine learning models are susceptible to adversarial attacks, requiring the testing of model and product robustness. Meanwhile, attackers also seek to automate malware generation and evasion of antivirus systems, and defenders try to gain insight into their methods. This work proposes a new algorithm that combines Malware Evasion and Model Extraction (MEME) attacks. MEME uses model-based reinforcement learning to adversarially modify Windows executable binary samples while simultaneously training a surrogate model with a high agreement with the target model to evade. To evaluate this method, we compare it with two state-of-the-art attacks in adversarial malware creation, using three well-known published models and one antivirus product as targets. Results show that MEME outperforms the state-of-the-art methods in terms of evasion capabilities in almost all cases, producing evasive malware with an evasion rate in the range of 32–73%. It also produces surrogate models with a prediction label agreement with the respective target models between 97–99%. The surrogate could be used to fine-tune and improve the evasion rate in the future.
Stealing and Evading Malware Classifiers and Antivirus at Low False Positive Conditions
Model stealing attacks have been successfully used in many machine learning domains, but there is little understanding of how these attacks work against models that perform malware detection. Malware detection and, in general, security domains have unique conditions. In particular, there are very strong requirements for low false positive rates (FPR). Antivirus products (AVs) that use machine learning are very complex systems to steal, malware binaries continually change, and the whole environment is adversarial by nature. This study evaluates active learning model stealing attacks against publicly available stand-alone machine learning malware classifiers and also against antivirus products.
A Study of Machete Cyber Espionage Operations in Latin America
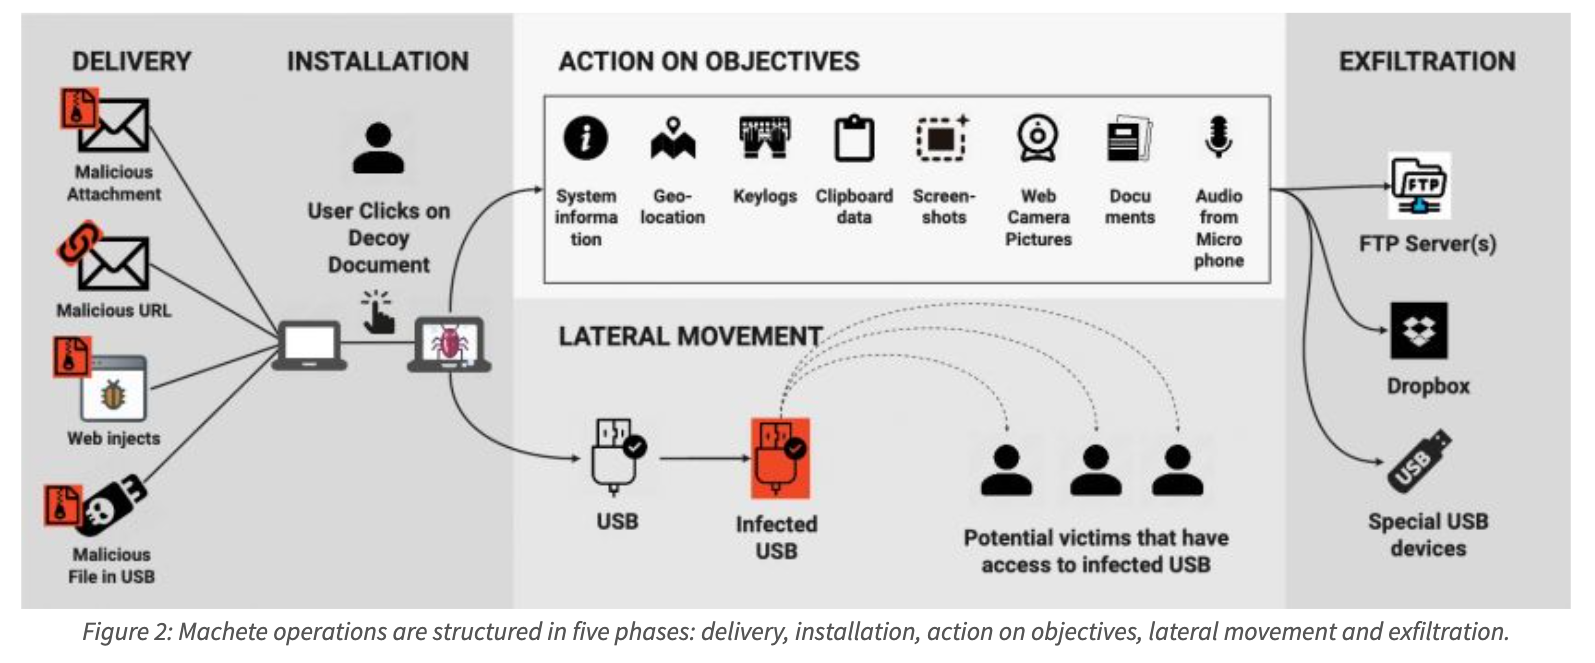
Our research shows that Machete is operated by a highly coordinated and organized group that focuses on Latin American targets. We describe the five phases of the APT operations from delivery to exfiltration of information and we show why Machete is considered a cyber espionage tool. Furthermore, our analysis indicates that the targeted victims belong to military, political or diplomatic sectors. The review of the almost eight years of Machete operations shows that it is probably operated by a single group whose activities may be state-sponsored. Machete is still active and operational to this day.
Detecting DNS Threats: A Deep Learning Model to Rule Them All
Domain Name Service is a central part of Internet regular operation. Such importance has made it a common target of different malicious behaviors such as the application of Domain Generation Algorithms (DGA) for command and control a group of infected computers or Tunneling techniques for bypassing system administrator restrictions. A common detection approach is based on training different models detecting DGA and Tunneling capable of performing a lexicographic discrimination of the domain names. However, since both DGA and Tunneling showed domain names with observable lexicographical differences with normal domains, it is reasonable to apply the same detection approach to both threats. In the present work, we propose a multi-class convolutional network (MC-CNN) capable of detecting both DNS threats. The resulting MC-CNN is able to detect correctly 99% of normal domains, 97% of DGA and 92% of Tunneling, with a False Positive Rate of 2.8%, 0.7% and 0.0015% respectively and the advantage of having 44% fewer trainable parameters than similar models applied to DNS threats detection.
Machete: Dissecting the Operations of a Cyber Espionage Group in Latin America
Reports on cyber espionage operations have been on the rise in the last decade. However, operations in Latin America are heavily under researched and potentially underestimated. In this paper we analyze and dissect a cyber espionage tool known as Machete. Our research shows that Machete is operated by a highly coordinated and organized group who focuses on Latin American targets. We describe the five phases of the APT operations from delivery to exfiltration of information and we show why Machete is considered a cyber espionage tool. Furthermore, our analysis indicates that the targeted victims belong to military, political, or diplomatic sectors. The review of almost six years of Machete operations show that it is likely operated by a single group, and their activities are possibly state-sponsored. Machete is still active and operational to this day.
Bringing a GAN to a Knife-Fight: Adapting Malware Communication to Avoid Detection.
Generative Adversarial Networks (GANs) have been successfully used in a large number of domains. This paper proposes the use of GANs for generating network traffic in order to mimic other types of traffic. In particular, our method modifies the network behavior of a real malware in order to mimic the traffic of a legitimate application, and therefore avoid detection. By modifying the source code of a malware to receive parameters from a GAN, it was possible to adapt the behavior of its Command and Control (C2) channel to mimic the behavior of Facebook chat network traffic. In this way, it was possible to avoid the detection of new-generation Intrusion Prevention Systems that use machine learning and behavioral characteristics. A real-life scenario was successfully implemented using the Stratosphere behavioral IPS in a router, while the malware and the GAN were deployed in the local network of our laboratory, and the C2 server was deployed in the cloud. Results show that a GAN can successfully modify the traffic of a malware to make it undetectable. The modified malware also tested if it was being blocked and used this information as a feedback to the GAN. This work envisions the possibility of self-adapting malware and self-adapting IPS.
Arming Malware with GANs
Generative Adversarial Networks (GANs) are a recent invention that shows impressive results in generating completely new images of faces, building interiors and much more. In this talk we present how we can use GANs to modify network traffic parameters in order to mimic other types of traffic. More specifically, we modify an open source malware to use a GAN to dynamically adapt its Command and Control network behavior and mimic the traffic characteristics of Facebook chat. In this way it is able to avoid the detection from new-generation Intrusion Prevention Systems that use behavioral characteristics. We will present our experiments from a real-life scenario that used the Stratosphere behavioral IPS deployed in a router between the malware which was deployed in our lab and the C&C server deployed in AWS. Results show that it is possible for the malware to become undetected when given the input parameters from a GAN. The malware is also aware of whether or not it is being blocked and uses this as a feedback signal in order to improve the GAN model. Finally, we discuss the implications of this work in malware detection as well as other areas such as censorship circumvention.